Designing a Safe & Seamless Sandbox → Production Promotion System
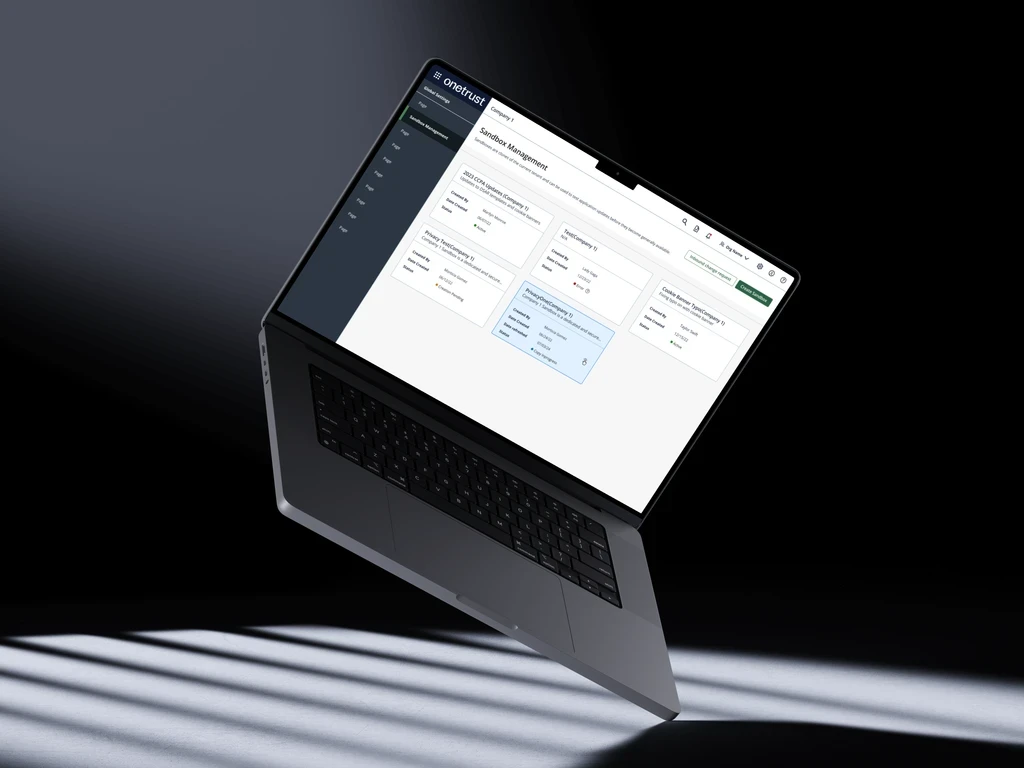
Enterprise customers had no safe staging environment, forcing them to test directly in production or manually recreate configurations across tenants. I led the design of an end-to-end promotion lifecycle that turned fragile imports into governed Change Requests.
 0.1 PRODUCT OVERVIEW
 0.2 IMAGE
 0.3 IMAGE
 0.4 IMAGE
 0.5 IMAGE
OneTrust had no native staging environment. Enterprise administrators had to build and test directly in production or spend dozens of hours manually recreating configurations between UAT and Prod. Fragile JSON/CSV bulk imports routinely failed, broke dependencies, and left governance teams blind.
- Teams spent 20+ hours per release manually rebuilding identical configs across environments.
- Bulk imports failed silently or caused runtime outages due to missing parent objects and circular references.
- Zero approval gates, version tracking, or rollback options meant teams operated in constant fear of breaking live privacy setups.
 0.1b PLATFORM CORE
Detailed architecture, user research, and technical walkthrough below ↓
Uncovering the Cost of Manual Recreation.
The brittle world of bulk imports.
Without an isolated staging environment, customers relied on error-prone file exports. Admins had to manually copy IDs, re-link rules, and pray that live production forms didn't crash during deployment.
- Audited support escalations linked to broken production privacy banners and DSAR forms
- Documented admin workarounds: dual-monitor copy-pasting between UAT and production
- Identified the technical boundaries of tenant cloning and database isolation
1.1 AUDIT"Tell Me What Will Break Before I Break It."
Listening to Tier-1 Power Users.
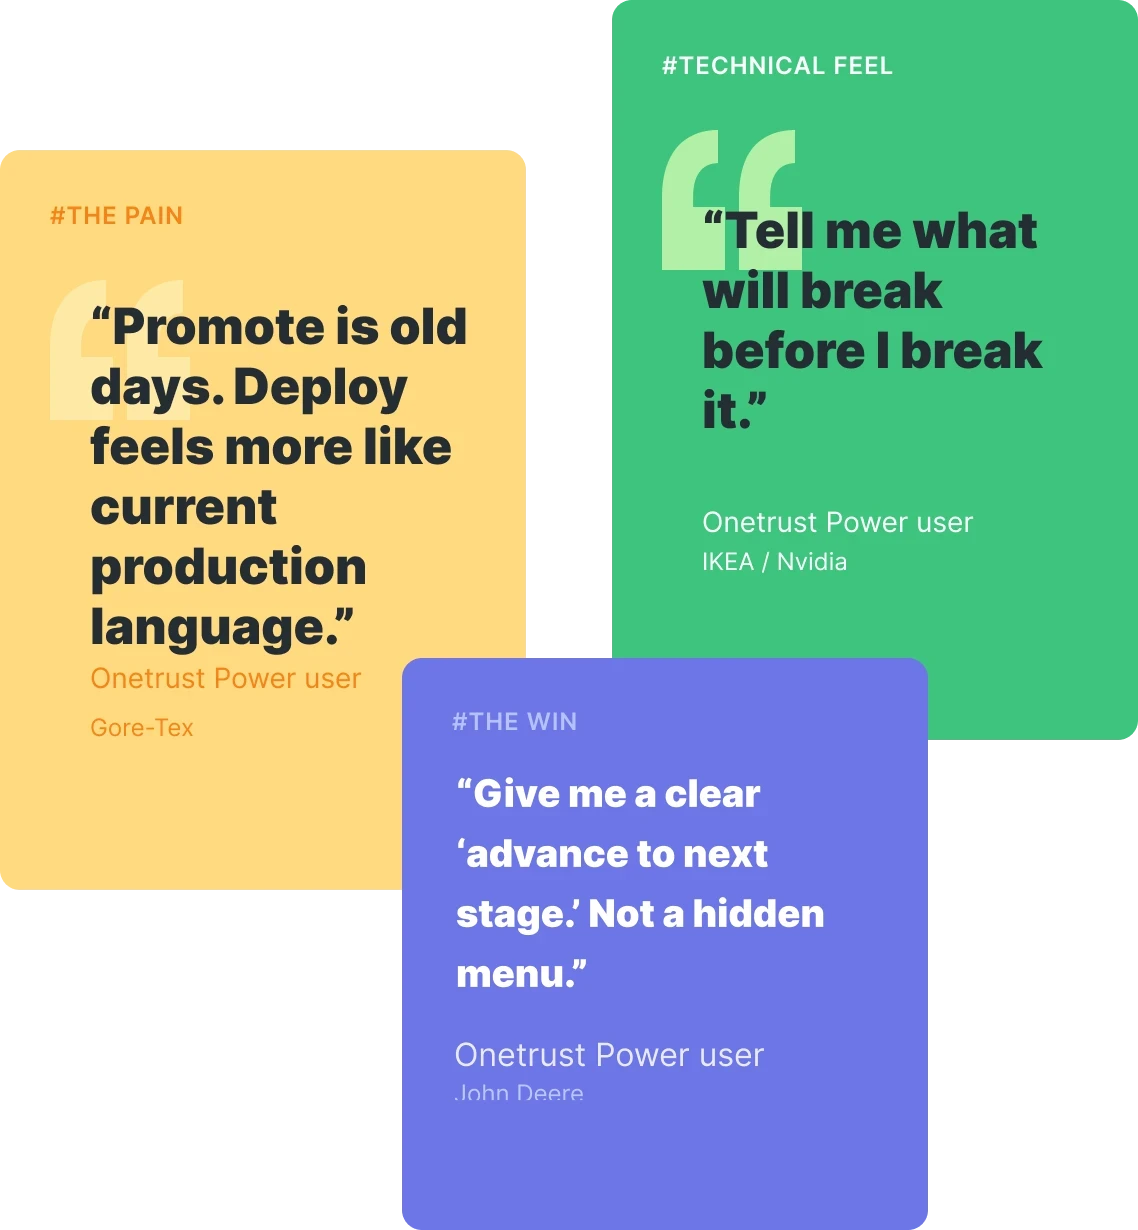
We interviewed enterprise leaders across Gore-Tex, IKEA, NVIDIA, and John Deere. Their demands were unanimous: they didn't just want a playground to test in; they needed a clear, governed highway to production.
- Gore-Tex: Pushed for real production vernacular — "Deploy" feels like software releases, whereas "Promote" felt obsolete.
- IKEA / NVIDIA: Demanded aggressive pre-flight checks: "Tell me what will break before I break it."
- John Deere: Emphasized workflow clarity: "Give me a clear 'advance to next stage' button, not a hidden menu."
 2.1 RESEARCH
The "Change Request" as the Atomic Unit of Promotion.
Moving beyond file uploads.
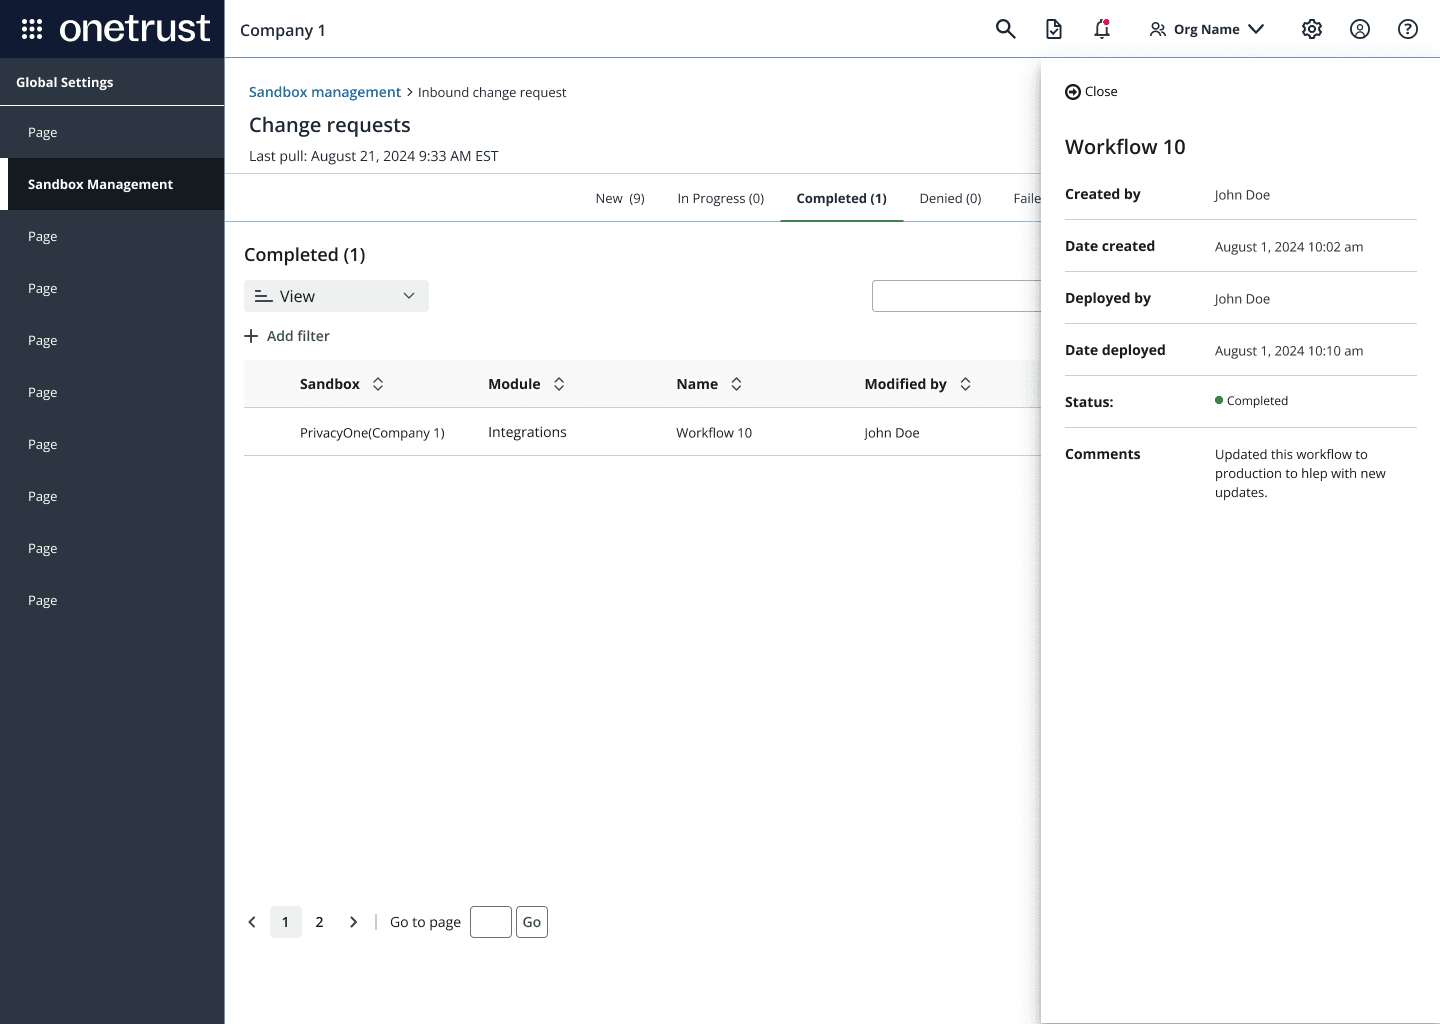
The architectural breakthrough was recognizing that configuration changes cannot be handled as loose files. By wrapping them in structured "Change Requests," we unlocked versioning, differential reviews, approvals, and rollback safety.
- Bundled multi-object edits (forms, workflows, templates) into an atomic Change Request
- Surfaced side-by-side environment diffs to preview exactly what would update or delete
- Embedded dependency graph inspections into the initial review drawer
 3.1 CONCEPT
Interactive Pre-Flight Dependency & Credential Mapping.
Designing for zero deployment surprises.
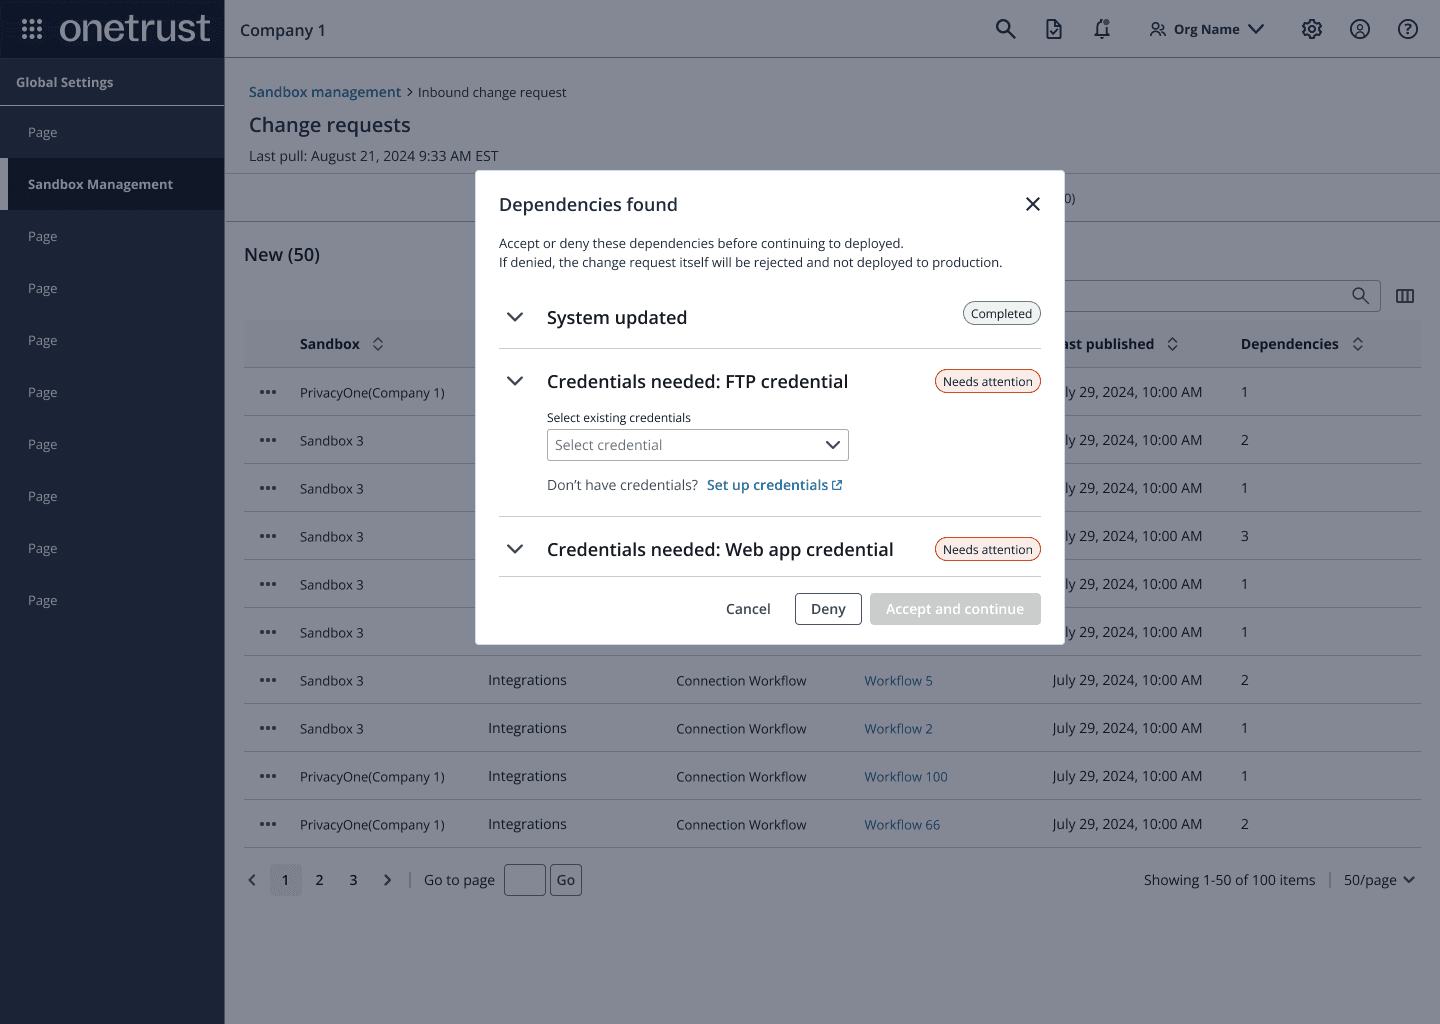
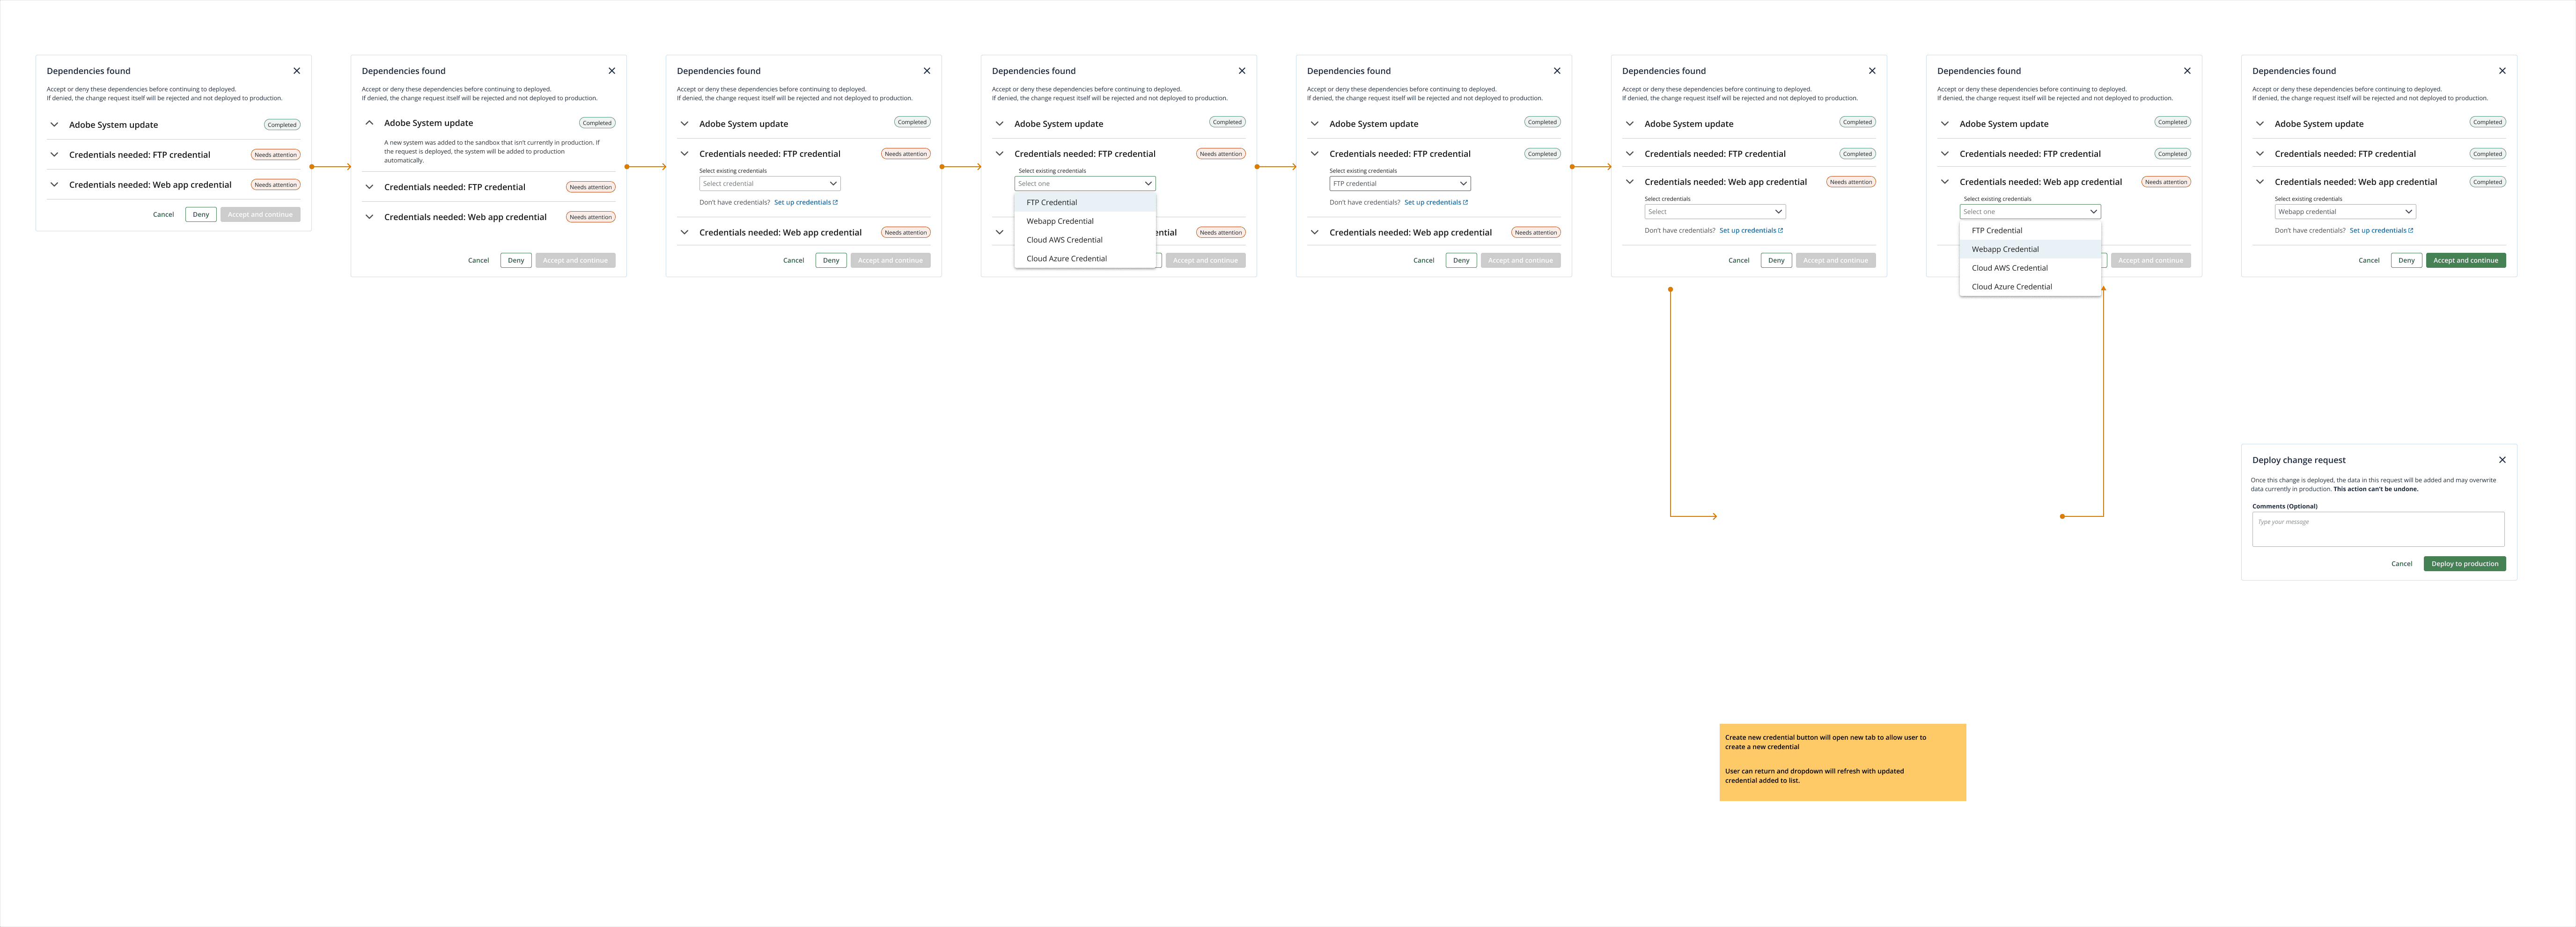
The hardest UX problem was managing missing dependencies and environment-specific credentials. We designed a step-by-step resolution modal that guides users through linking required API keys, FTP credentials, and parent systems before deployment.
- Mapped out comprehensive edge-case flows for missing dependencies and unauthenticated webhooks
- Designed inline credential selectors allowing admins to map production secrets without leaving the flow
- Surfaced clear warning banners highlighting that production data could be overwritten
4.1 FLOW MAP4.2 MODAL UI4.3 INTERACTIONReview, Approval Signoff, and Production Launch.
The final deployment gate.
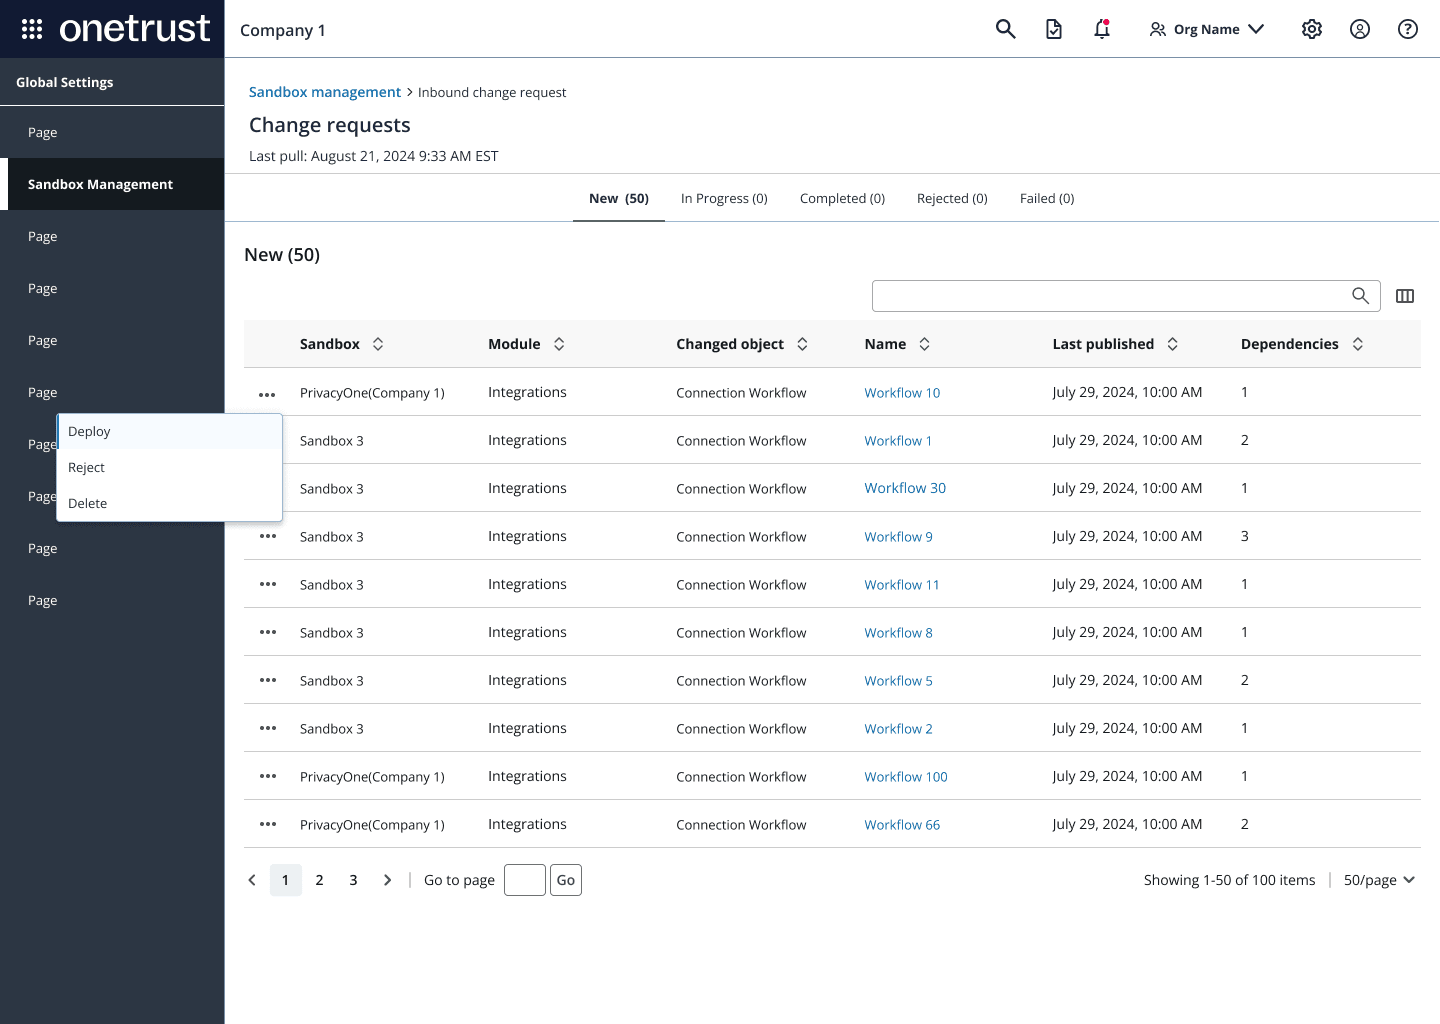
Before any package is pulled into production, the system presents an explicit review summary. Admins provide mandatory change reasons, review impacted objects, and pull changes with full audit trace integrity.
- Final confirmation modal enforcing structured change rationale documentation
- Deployed outbound tracking table showing publish timestamps, change types, and details
- Shipped to enterprise customers with universal positive feedback from security and compliance teams
 5.1 CONFIRMATION5.2 AUDIT LOG6.1 BEFORE
- Manual rebuilding of configurations across UAT and production tenants
- Brittle JSON/CSV exports that crashed on hidden dependencies and circular references
- Zero peer review, approval governance, or audit trail before deployment
Pre-flight dependency detection completely transformed user sentiment. Surfacing missing child objects and unmapped credentials before anything touches production eliminated the fear factor.
Handling partial promotions vs. atomic rollbacks. When a complex package had 20 sub-workflows and one failed, designing a graceful partial state without leaving production in an inconsistent limbo was technically challenging.
The Sandbox & Promotion system replaced hours of stressful, manual rework with a predictable 6-stage lifecycle. By pairing tenant cloning with automated pre-flight checks and Change Request approvals, enterprise customers like Gore-Tex, IKEA, NVIDIA, and John Deere can innovate rapidly in sandbox and promote to production with complete peace of mind.